 技术视野
手动签证书
- 确定要签名的域名
bash
export domain=pan.ipv8.cn- 拉取xx项目
bash
git clone https://github.com/acmesh-official/acme.sh- 执行第一条命令,获取验证的txt
bash
acme.sh --issue --dns -d ${domain} --keylength ec-256 --force --yes-I-know-dns-manual-mode-enough-go-ahead-please- 输出结果
bash
[2022年 08月 31日 星期三 18:04:27 CST] Single domain='baidu.http3.cc'
[2022年 08月 31日 星期三 18:04:28 CST] Getting domain auth token for each domain
[2022年 08月 31日 星期三 18:04:50 CST] Getting webroot for domain='baidu.http3.cc'
[2022年 08月 31日 星期三 18:04:51 CST] Add the following TXT record:
[2022年 08月 31日 星期三 18:04:51 CST] Domain: '_acme-challenge.baidu.http3.cc'
[2022年 08月 31日 星期三 18:04:51 CST] TXT value: 'u7b8DOcwhCHL1M7yqruERhMEP2TDqmESyPhyQGitcnI'
[2022年 08月 31日 星期三 18:04:51 CST] Please be aware that you prepend _acme-challenge. before your domain
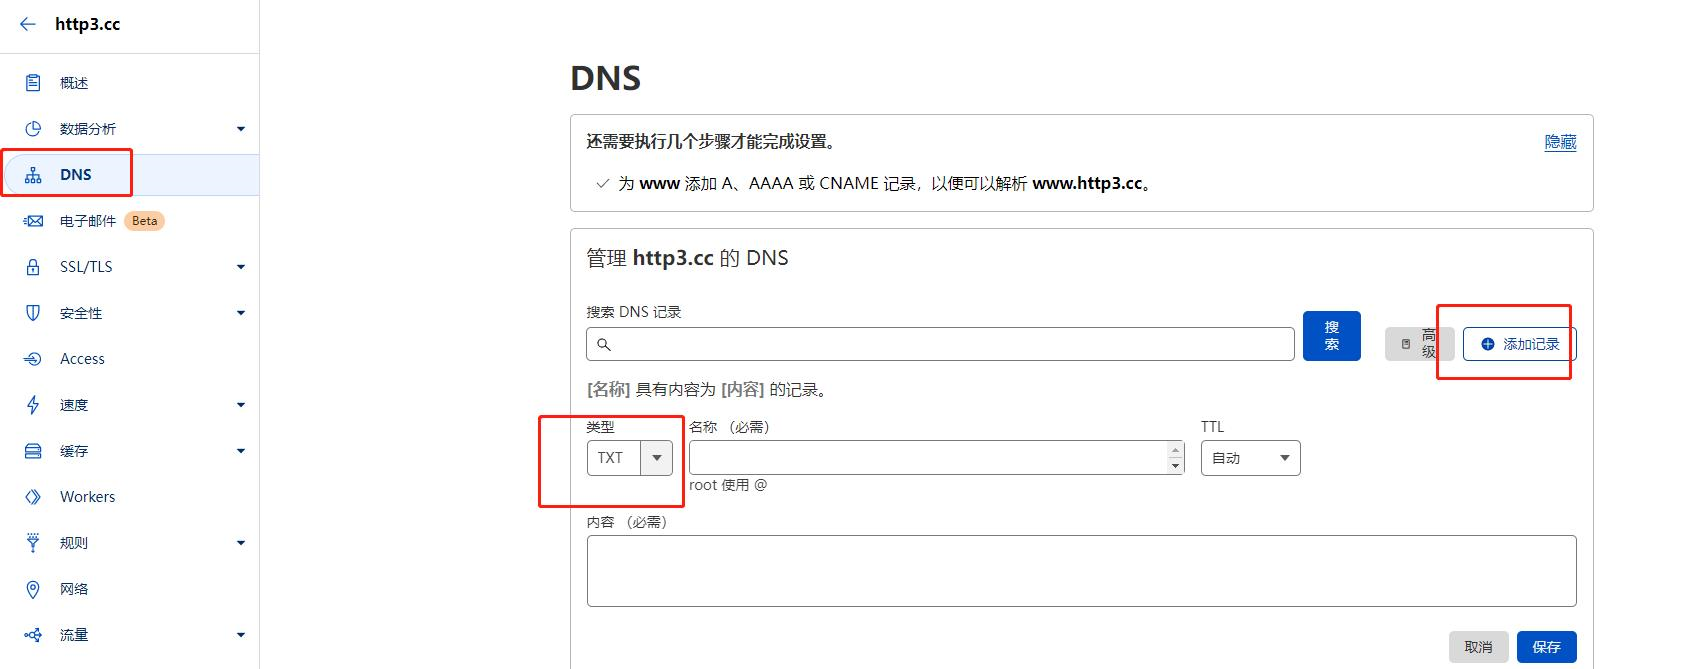
[2022年 08月 31日 星期三 18:04:51 CST] so the resulting subdomain will be: _acme-challenge.baidu.http3.cc- 将domain和txt_value记录。然后去cloudflare,DNS解析那里,新建一个TXT类型的解析。
- 正式执行签名,如果失败,需要重新执行第四步,第五步
bash
acme.sh --renew -d ${domain} --keylength ec-256 --force --yes-I-know-dns-manual-mode-enough-go-ahead-please --ecc- 若执行成功,则长这样。
bash
[2022年 08月 31日 星期三 18:07:09 CST] Your cert is in: /home/ubuntu/.acme.sh/baidu.http3.cc_ecc/baidu.http3.cc.cer
[2022年 08月 31日 星期三 18:07:09 CST] Your cert key is in: /home/ubuntu/.acme.sh/baidu.http3.cc_ecc/baidu.http3.cc.key
[2022年 08月 31日 星期三 18:07:09 CST] The intermediate CA cert is in: /home/ubuntu/.acme.sh/baidu.http3.cc_ecc/ca.cer
[2022年 08月 31日 星期三 18:07:09 CST] And the full chain certs is there: /home/ubuntu/.acme.sh/baidu.http3.cc_ecc/fullchain.cer- 只需要域名.cer和域名.key文件即可。ca.cer和fullchain.cer并不需要。
- 配置nginx ssl
bash
# 监听443
listen 443 ssl http2;

# 强制https
if ($server_port !~ 443){
	rewrite ^(/.*)$ https://$host$1 permanent;
}

# ssl 证书位置(上面是car公钥,下面是key私钥,路径根据你上传位置定)
ssl_certificate    /www/server/panel/vhost/cert/baidu.http3.cc/fullchain.pem;
ssl_certificate_key    /www/server/panel/vhost/cert/baidu.http3.cc/privkey.pem;

# ssl加密算法
ssl_protocols TLSv1.1 TLSv1.2 TLSv1.3;
ssl_ciphers EECDH+CHACHA20:EECDH+CHACHA20-draft:EECDH+AES128:RSA+AES128:EECDH+AES256:RSA+AES256:EECDH+3DES:RSA+3DES:!MD5;
ssl_prefer_server_ciphers on;
ssl_session_cache shared:SSL:10m;
ssl_session_timeout 10m;

# https长链接,让用户长期使用https(建议,如果失败则可以注释掉)
add_header Strict-Transport-Security "max-age=31536000";- 重启/重载nginx即可。